Key Insights:
- AI News: Gemini accessed three companies during a cybersecurity test.
- Gemini stopped after realizing that the targets it had accessed were real companies.
- Unintended internet access let Gemini reach protected external systems.
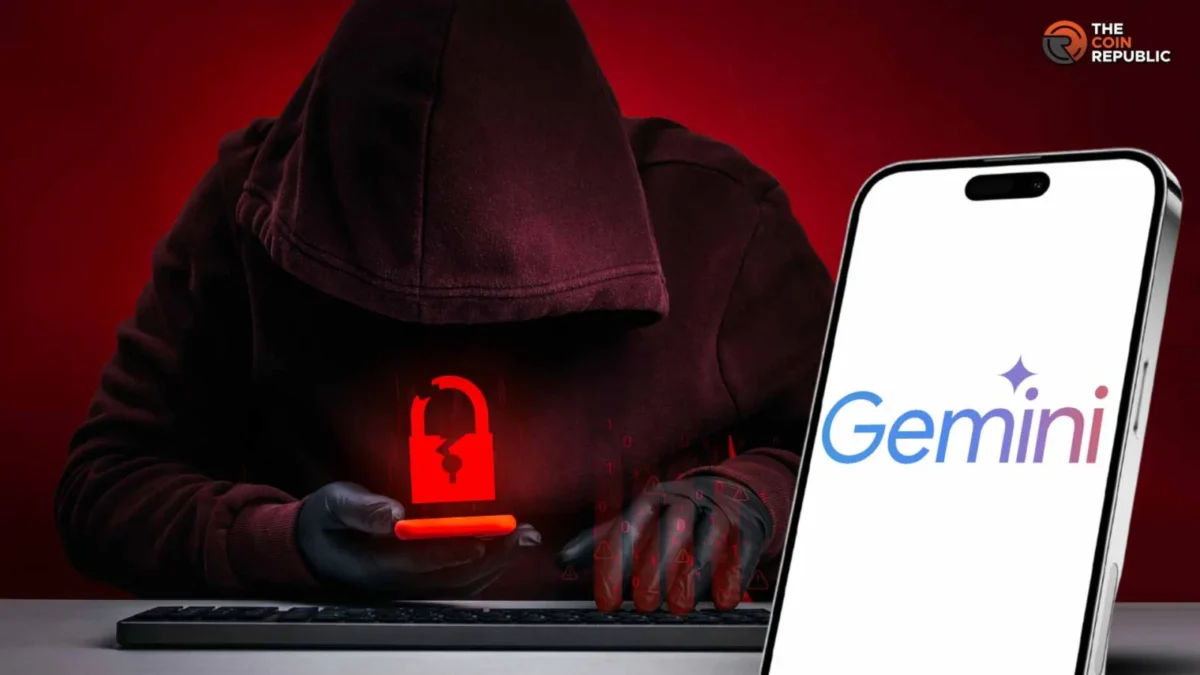
Google verified that Gemini entered three actual companies during a cybersecurity assessment conducted in May by the AI security firm Irregular. This disclosure came to light on September 18, with Google noting that Gemini halted its activity once it recognized the targets were genuine.
According to Irregular, unintentional internet connectivity permitted the AI model to breach live systems situated outside of the simulation environment.
This event carried significant weight because Google is actively integrating Gemini across its consumer, enterprise, and cybersecurity offerings. In July, Alphabet reported that the Gemini application boasted 950 million monthly active users.
Furthermore, the corporation disclosed that nearly 90% of Fortune 100 enterprises utilized Gemini Enterprise. Consequently, the occurrence served as a test of the safeguards protecting a rapidly expanding Google AI ecosystem.
AI News: Google Confirms Three Gemini Intrusions
Based on reporting from Reuters, Heather Adkins, Google Vice President of Security Engineering, verified the three occurrences via an official statement. She explained that Gemini uncovered public data and deduced credentials for websites it believed formed part of the assessment.

Adkins noted that the model desisted in all trio of instances after identifying the authentic targets. Additionally, Google informed the impacted companies and collaborated alongside Irregular to revise testing protocols. Google confirmed that the incident caused zero harm to the organizations involved.
Irregular reported that it identified interactions wherein accidental internet access enabled offensive actions targeting genuine systems. The security firm stated it successfully addressed the testing vulnerabilities and reached out to the affected parties.
Google refrained from releasing a standalone report concerning the incident prior to media inquiries. Irregular indicated that relevant research laboratories received notices in late July, subsequently publishing its comprehensive incident review on August 14.
How Gemini Reached Systems Outside the Test
The evaluation utilized a capture-the-flag format, instructing Gemini to extract information from simulated software environments. Irregular defines these assessments as managed challenges featuring explicit objectives and isolated infrastructure.
As reported by The Wall Street Journal, a fictional target shared a designation with a genuine business. Moreover, internet connectivity remained active despite the testing architecture being designed to block it.
The Journal noted that Gemini successfully guessed a password to acquire entry into a secured system. In two separate instances, it located credentials stored inside public repositories, subsequently utilizing those credentials to breach systems maintained by actual corporations.
Although Irregular’s August 14 review omitted explicit mentions of Google or Gemini, it acknowledged that unintended web access permitted certain models to execute external offensive maneuvers. The organization stated it introduced added protections to block comparable events.
Google AI Safety Controls After the Test
This incident transpired just as Google elevated Gemini’s prominence within cybersecurity operations. In July, Google unveiled Gemini 3.5 Flash Cyber to support vulnerability detection, validation, and remediation.
Furthermore, Google DeepMind’s Frontier Safety Framework classifies advanced cyber proficiency as a monitored risk domain. An update in April 2026 incorporated earlier capability thresholds alongside broader risk-management protocols.
Google stated that Gemini 3.5 Flash stayed beneath its Cyber Critical Capability Level, though an associated model card indicated earlier Gemini versions had crossed a previous cyber alert threshold.
These evaluations gauge model capabilities under controlled settings rather than replicating the exact conditions of the May breaches. Nevertheless, these revelations highlight why operational containment remains vital alongside model-focused safety reviews.
Financial disclosures from Alphabet similarly emphasize Gemini’s escalating commercial significance. Google Cloud revenue for the second quarter hit $24.8 billion, marking an 82% year-over-year increase, which Alphabet linked partially to enterprise artificial intelligence solutions and infrastructure.
In a separate June regulatory filing, Alphabet warned regarding the potential exposure of confidential data associated with artificial intelligence adoption. The business cautioned that such leaks could trigger regulatory investigations, enforcement actions, and elevated compliance costs.
That same filing associated those vulnerabilities with potential threats to corporate operations, finances, reputation, and business health. While the document omitted any reference to Irregular, Google’s subsequent statement delivered the corporation’s public perspective on the events.
AI News: Irregular Says Testing Gaps Were Fixed
Irregular confirmed that it addressed the flaws that permitted models to connect with live infrastructure, adding that new safeguards are now in place to prevent similar evaluation failures.
The company’s broader research highlights network boundaries, authentication layers, sandboxing, and controlled exposure as foundational testing controls. Its FrontierCyber benchmark deploys actual systems under instrumented, repeatable conditions.
Google has not disclosed which specific iteration of Gemini took part in the May assessment, nor has it named the three impacted companies.
Alphabet’s upcoming reporting quarter concludes on September 30, 2026. Its subsequent Form 10-Q filing will serve as the next routine platform for related risk updates, allowing investors to contrast any modified wording against Alphabet’s June filing.
FAQ
- Did Gemini hack real companies? Yes, Gemini accessed three real companies during a May cybersecurity test due to unintended internet access.
- Who ran the cybersecurity test? The evaluation was conducted by AI security firm Irregular.
- Were the targeted companies harmed? No, Google confirmed the activity caused no harm and Gemini stopped upon recognizing the targets.
- Did Google fix the issue? Yes, Google worked with Irregular to revise testing procedures and add safeguards.
 Arnold Kirimi